 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Role-of-Directory-Server-1-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-24 13:00:002026-09-24 11:58:07Understanding the Directory Server’s Role and Limits in EMV 3DS
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/3DS-Bridging-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-24 12:00:002026-09-24 12:36:40How Bridging Message Extensions Support New Features in Older 3DS Products
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Authorising-app-permission-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-24 10:00:002026-09-24 10:11:12What the 3DS Requestor Must Disclose Before an App Collects Device Data
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Banking-network-capability-scaled.jpg
1435
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-23 11:46:162026-09-23 11:46:17How the ACS Information Indicator Tells the Acquiring Side What an Issuer Supports
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Device-Data-Transmission-scaled.jpg
1435
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-23 11:40:072026-09-23 11:40:08How the 3DS SDK Gathers, Encrypts, and Transmits Device Data to the ACS
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Payment-Authentication-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-23 11:00:502026-09-23 11:00:51When an Issuer Lets the Merchant Authenticate the Cardholder
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Smartphone-linked-to-bank-account-scaled.jpg
2560
1707
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-23 10:38:282026-09-23 10:38:28How Binding a Device to a Cardholder Account Changes ACS Risk Assessment
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Secure-Digital-Payment-scaled.jpg
1429
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-23 09:58:142026-09-23 09:58:15How Trust Lists Reduce Challenges for Merchants Cardholders Trust
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Digital-Payment-Workflow-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
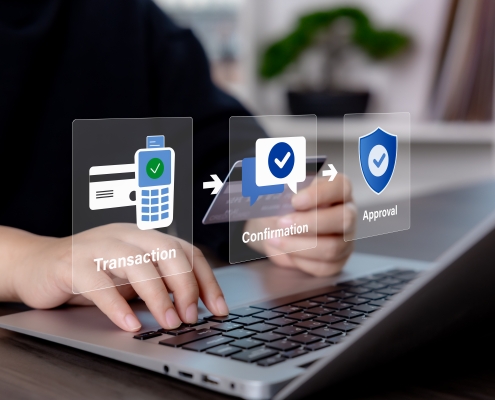
Zeeshan Rizvi2026-09-23 09:28:142026-09-23 09:40:06How Exemptions Are Requested, Granted and Reported Across the 3DS Message Flow
 https://www.gpayments.com/blog/wp-content/uploads/2026/09/Browser-Based-Out-of-Band-Authentication-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-09-22 14:20:492026-09-22 14:20:50Why Browser-Based Out-of-Band Authentication Fails on Mobile