Tag Archive for: 3d secure
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/PCI-3DS-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-20 11:42:032026-10-20 11:42:04What a PCI 3DS Assessment Covers for ACS and 3DS Server Operators
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/Card-payments-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-16 15:31:312026-10-16 15:31:32How to Authenticate Stored-Card Payments When Account Takeover Is Suspected
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/One-3DS-Server-Multiple-Acquirers-scaled.jpg
2560
1928
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-16 10:22:222026-10-16 10:22:23Using One 3DS Server Across Multiple Acquirers
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/RBA-Review-Feedback-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-15 09:42:512026-10-15 09:43:20What the RBA Review Feedback Means for Card-Not-Present Authentication
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/3DS-Challenge-Indicator-Value-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-14 10:29:282026-10-14 10:29:29When Merchants Should Request a 3DS Challenge, and When to Ask for None
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/SMS-OTP-scaled.jpg
1528
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-14 09:50:162026-10-14 09:50:17What Regulators Retiring SMS OTPs Means for 3D Secure Challenges
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/3D-Secure-Authentication-Flow.png
887
1774
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
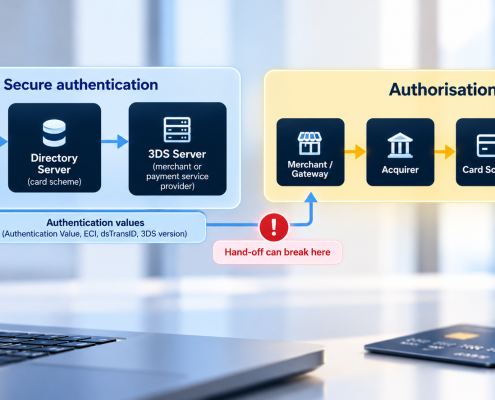
Zeeshan Rizvi2026-10-13 13:55:352026-10-13 15:12:10Why Authenticated Transactions Lose Their 3D Secure Protection at Authorisation
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/Card-Payment-Authorisation-scaled.jpg
1703
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-12 13:30:002026-10-20 11:33:27How Issuers Should Use 3DS Results When the Authorisation Arrives
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/Letter-of-Approval-scaled.jpg
1435
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-12 10:57:002026-10-20 11:27:43What an EMVCo Letter of Approval Means for a 3DS Product
 https://www.gpayments.com/blog/wp-content/uploads/2026/10/Peak-trading-scaled.jpg
1707
2560
Zeeshan Rizvi
https://blog.gpayments.com/wp-content/uploads/2022/05/Logo_Black_on_White_lowres-300x80.png
Zeeshan Rizvi2026-10-09 10:00:192026-10-09 10:00:21How to Prepare Your 3D Secure Authentication for Peak Trading